


DHCP and DNS as part of Security Flows
February 2014, At the RSA 2014 conference in San Francisco, a great deal of the discussion was on the management and threat reduction due to changes in the DHCP and DNS protocols and their attacks by malware & outside network services. These changes include support for IPV6 and legacy IPV4 devices on the same network.
IPV6 networks do not include full legacy compatibility with IPV4 devices, and in most cases the DNS protocol is for an externally facing IPC4 address with an internal IPV6 tunnel. This setup creates a scenario for the DNS protocol tp be easily exploited by hackers. In most systems layered security, next-generation firewalls, and secure web gateways are not designed to protect DNS. These are attackable by an extensive arsenal of attacks such as “DrDos” and “DNS cache poisoning” in addition to DDoS attacks.
Infoblox DNS Firewall
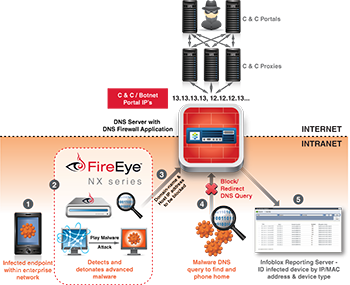
At the event, Infoblox was showing their DNS management tools and dedicated appliances that include DNS firewalls. The Infoblox DNS Firewall integration with FireEye NX Series appliance uses the FireEye Multi-Vector Virtual Execution (MVX) engine and delivers defense against Advanced Persistent Threats (APT) for networks. The DNS Firewall works by automatically disrupting malware communication attempts with Internet-based domains. This solution allows for defining of hierarchical policies –block, redirect, pass-through and log to meet IT processes for handling APT communication.
These issues will be escalating in importance and visibility as new security appliances and cloud service centers get added to existing IPV4 equipment. There are already many systems issues for mixed IPV4 and IPV6 networks, and security is one of the next challenges.
